01
Connect, pick a branch, scan.
Install the Rectify GitHub App with read-only access, choose a repository and a branch, and scan the whole repo. Progress shows live, from queued to fetched, analysed and processed.
Features/Understand and fix
Code Scan
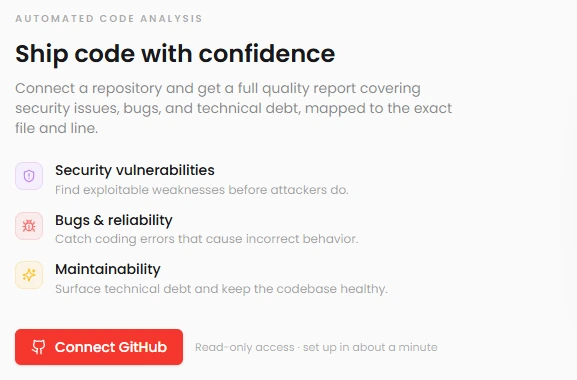
Connect GitHub, pick a branch, and get a report on bugs, security vulnerabilities and code smells in minutes. Then ask Quanta to explain any of it.
AI writes your code faster than anyone can review it. Somewhere in there is an exposed key, and nobody has looked.
Code Scan reads every line.
Install the Rectify GitHub App with read-only access, choose a repository and a branch, and scan the whole repo. Progress shows live, from queued to fetched, analysed and processed.
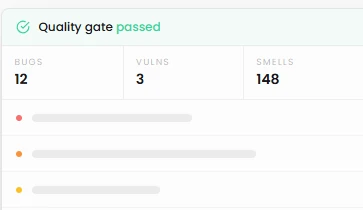
Summary tiles for bugs, vulnerabilities and code smells, with quality ratings, duplication and lines of code stored for every scan. Browse issues by severity, from Blocker to Info, by type or by search. Open any issue to see the rule, the root cause, how to fix it and the code around it.
40export async function charge(cart) {
41 const total = sum(cart.items)
42 const stripe = new Stripe("sk_live_51NcX…")
43 return stripe.charges.create({ amount: total })
A live Stripe key is committed to the repository, so anyone with read access can use it.
Move it to an environment variable such as STRIPE_SECRET_KEY, then rotate the key.
Quanta shows the top issues, starts a new scan and builds a PDF report you can share with the team. AI assistants connected over MCP, like Cursor and Claude Code, can start scans and read the results too.
Ask Quanta
Ask in plain English and Quanta does the work. Anything that changes your data waits for a person to approve it.
What’s the worst thing in my code right now?
One critical vulnerability: an API key exposed in lib/billing.ts, line 42. Then two major bugs in the sign-in flow. Want the details?
Scan the main branch again.
Starting a scan of main. I’ll tell you when it’s done.
Make a PDF for the team.
Code Scan report ready: 12 bugs, 3 vulnerabilities and 148 code smells, with the top issues first.
Everything in it
Free for 14 days. Set up in about two minutes.